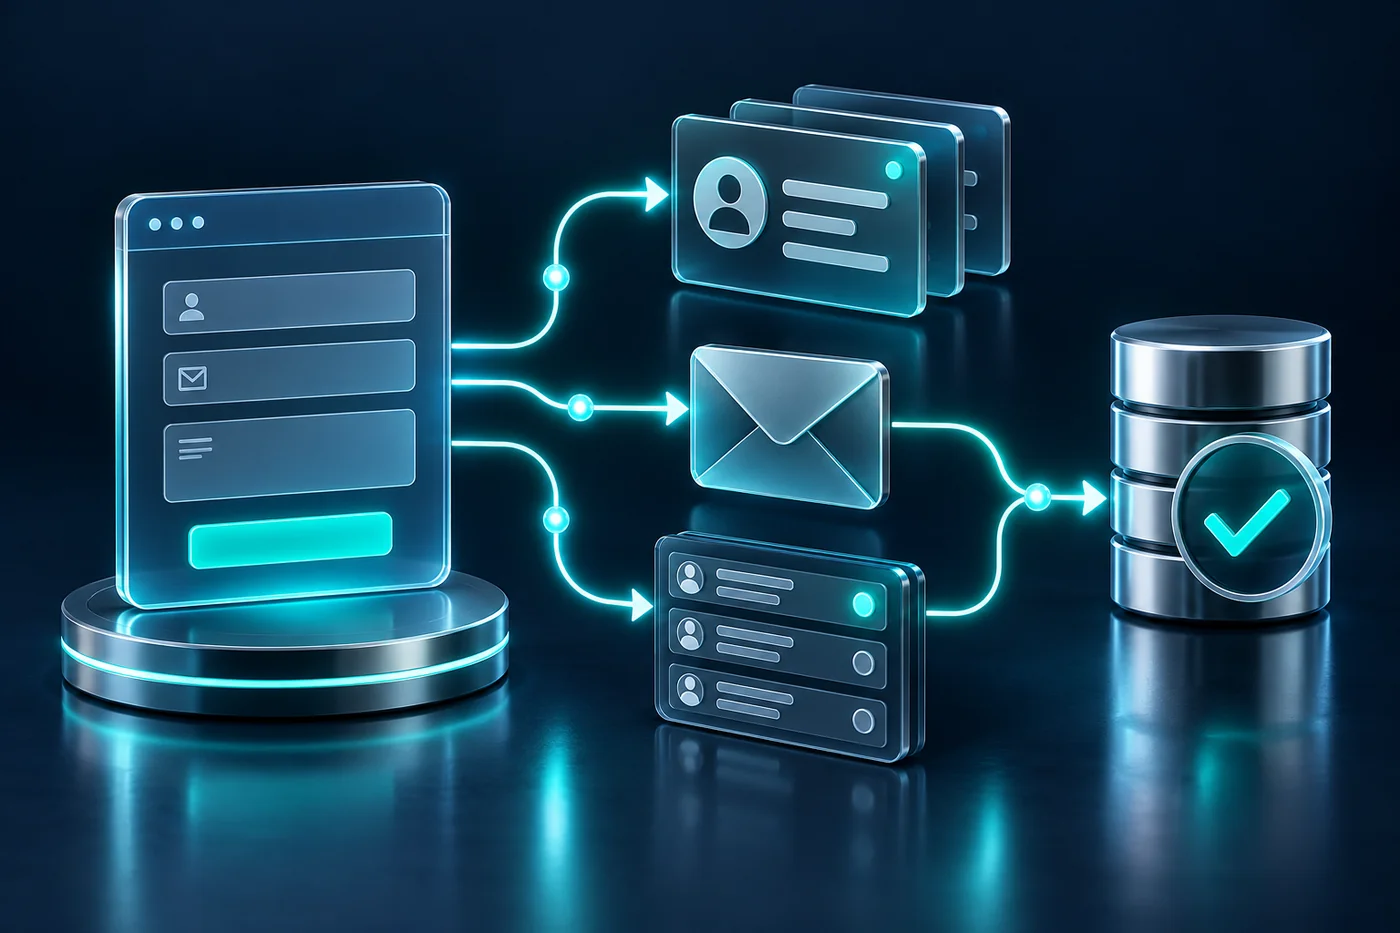
A website enquiry often passes through several systems: the form, a database, an email notification, a CRM, and a staff workflow. Automation can reduce repeated copying, but it also introduces new places where a request can fail or be processed twice.
A dependable workflow begins with a clear definition of what has been accepted and where the authoritative record lives. This guide explains how to plan enquiry automation that is observable, recoverable, and proportionate to a small business’s needs.
Draw the existing process before automating it
Follow one enquiry from submission to reply. Identify which system receives it first, who is notified, where staff record its status, and what happens when someone is unavailable. Include manual steps that people perform outside the website.
Look for unnecessary duplication and unclear ownership. If two people receive the message but neither is responsible for responding, automation may make the confusion faster rather than solving it.
Define the business outcome: a valid enquiry is accepted once, reaches the appropriate person, and has a visible follow-up status. That outcome is more useful than “connect the form to every available tool.”
Choose the authoritative record
Decide where the accepted enquiry is stored and how staff can recover it if a notification fails. An email can alert the team, but it may not be the best sole record of the request. A CRM or a private enquiry store can provide clearer status and recovery.
The visitor’s success message should correspond to acceptance by that authoritative system. A downstream notification failure should not necessarily make the website claim that the entire submission failed.
Our form delivery guide explains why delivery confirmation and interface feedback need to agree. Automation should preserve that distinction instead of hiding it behind several integrations.
Map fields explicitly
Document how each form field maps to the receiving system. Names, email addresses, service interests, and project descriptions should not be guessed from position or label text. A future form edit can otherwise send information into the wrong destination field.
Validate required values before creating the record. Keep optional fields optional throughout the workflow rather than replacing missing values with misleading placeholders. Normalise data only where the transformation is understood and useful.
Avoid sending every collected field to every connected tool. The notification system, CRM, and analytics service may need different information. Define each destination’s purpose separately.
Design duplicate handling
Visitors can submit twice, browsers can retry requests, and integrations can deliver the same event more than once. The workflow should recognise a repeated event where possible instead of creating duplicate leads every time.
Use a stable submission identifier or another deliberately designed idempotency approach. The receiving process should be able to tell whether it has already handled that event. An email address alone is usually insufficient because the same person may make a legitimate later enquiry.
Decide how a repeated request is acknowledged. It should not produce contradictory visitor messages or repeatedly notify staff about the same accepted event.
Plan retries without creating loops
Temporary failures can justify a retry, but retries need limits and a recorded outcome. Define which errors are retryable, how many attempts are allowed, and when staff should intervene. A malformed request should not be retried indefinitely.
Keep the original accepted record available while downstream work is pending. If a CRM is temporarily unavailable, the business should still have a way to find the enquiry and understand its state.
Avoid chaining integrations in a circular arrangement where one update triggers another and then feeds back into the first system. Document the direction of each event and which changes are allowed to initiate work.
Secure webhook and API boundaries
Treat incoming events as untrusted until they have been authenticated and validated through the provider’s supported mechanism. Keep credentials and signing secrets outside public website files and avoid including them in logs or client-side scripts.
Use appropriate transport protection, access controls, and request validation. The OWASP REST Security guidance provides a technical reference for reviewing API boundaries. The exact implementation depends on the provider and the workflow.
Limit permissions to the operations the integration needs. A form-to-CRM connection should not receive broad administrative access simply because it is convenient during setup.
Make failure states visible to the team
Create a clear status model such as accepted, notification pending, CRM pending, assigned, and replied. The precise labels can vary, but staff need to understand what has happened and what requires action.
Record operational identifiers, timestamps, and error categories without unnecessarily copying private message contents into technical logs. A useful log helps locate the problem while limiting exposure of customer information.
Define alerting around actionable failures. An alert for every temporary retry can overwhelm the team, while no alert at all can hide a growing queue of unprocessed enquiries.
Keep analytics separate from enquiry content
Marketing reporting can record that a valid enquiry was accepted without receiving the visitor’s message or email address. Use a deliberately defined event and avoid duplicating it through several systems.
If the website and CRM both report the same lead event, decide how the measurement system avoids counting it twice. Do not assume that all integrations use the same definition of a conversion.
Our GA4 lead tracking guide explains how to measure confirmed outcomes. Automation should support that definition rather than changing it accidentally.
A worked small-business workflow
Imagine a consultancy whose form stores an enquiry privately, sends an email alert, and creates a CRM task. The private record receives a unique identifier at acceptance. The email and CRM steps use that identifier so repeated deliveries can be recognised.
If email succeeds but the CRM is unavailable, the enquiry remains accepted and the CRM task is marked pending. A limited retry process handles the temporary issue, while staff can still locate the original record. The visitor receives one accurate confirmation rather than several conflicting messages.
This structure is intentionally simple. A smaller business may not need a CRM at all, but it still benefits from clear acceptance, recovery, and responsibility.
Test the awkward cases before launch
Test a valid enquiry, missing required information, duplicate delivery, a downstream timeout, and a failed notification. Use test records that are clearly identified and do not trigger unintended customer communication.
Confirm that staff understand the resulting statuses and can recover the request. A workflow is not complete merely because the happy path succeeds once. The failure paths are where operational clarity matters most.
Keep a recovery and rollback plan for integration changes. Document the existing connection before replacing it so the business does not lose a working route while experimenting.
Assign ownership after the build
Someone must review failures, manage credentials, maintain field mappings, and update the workflow when services or forms change. Include these responsibilities in the website handover rather than treating automation as maintenance-free.
Start with the smallest workflow that solves the actual problem. If you want to connect your website enquiries with a dependable follow-up process, contact Ali Dev Solutions and describe the tools and team involved.